nginx2root: Five nginx Flaws Put Millions of Servers on a Patch Clock
Key points
- On November 18, 2026, F5 and nginx.org disclosed ten nginx vulnerabilities, five of which form the nginx2root set from the Xint research team, with each CVE rated High (CVSS 3.1: 8.1) and Critical (CVSS 4.0: 9.2) by F5 1.
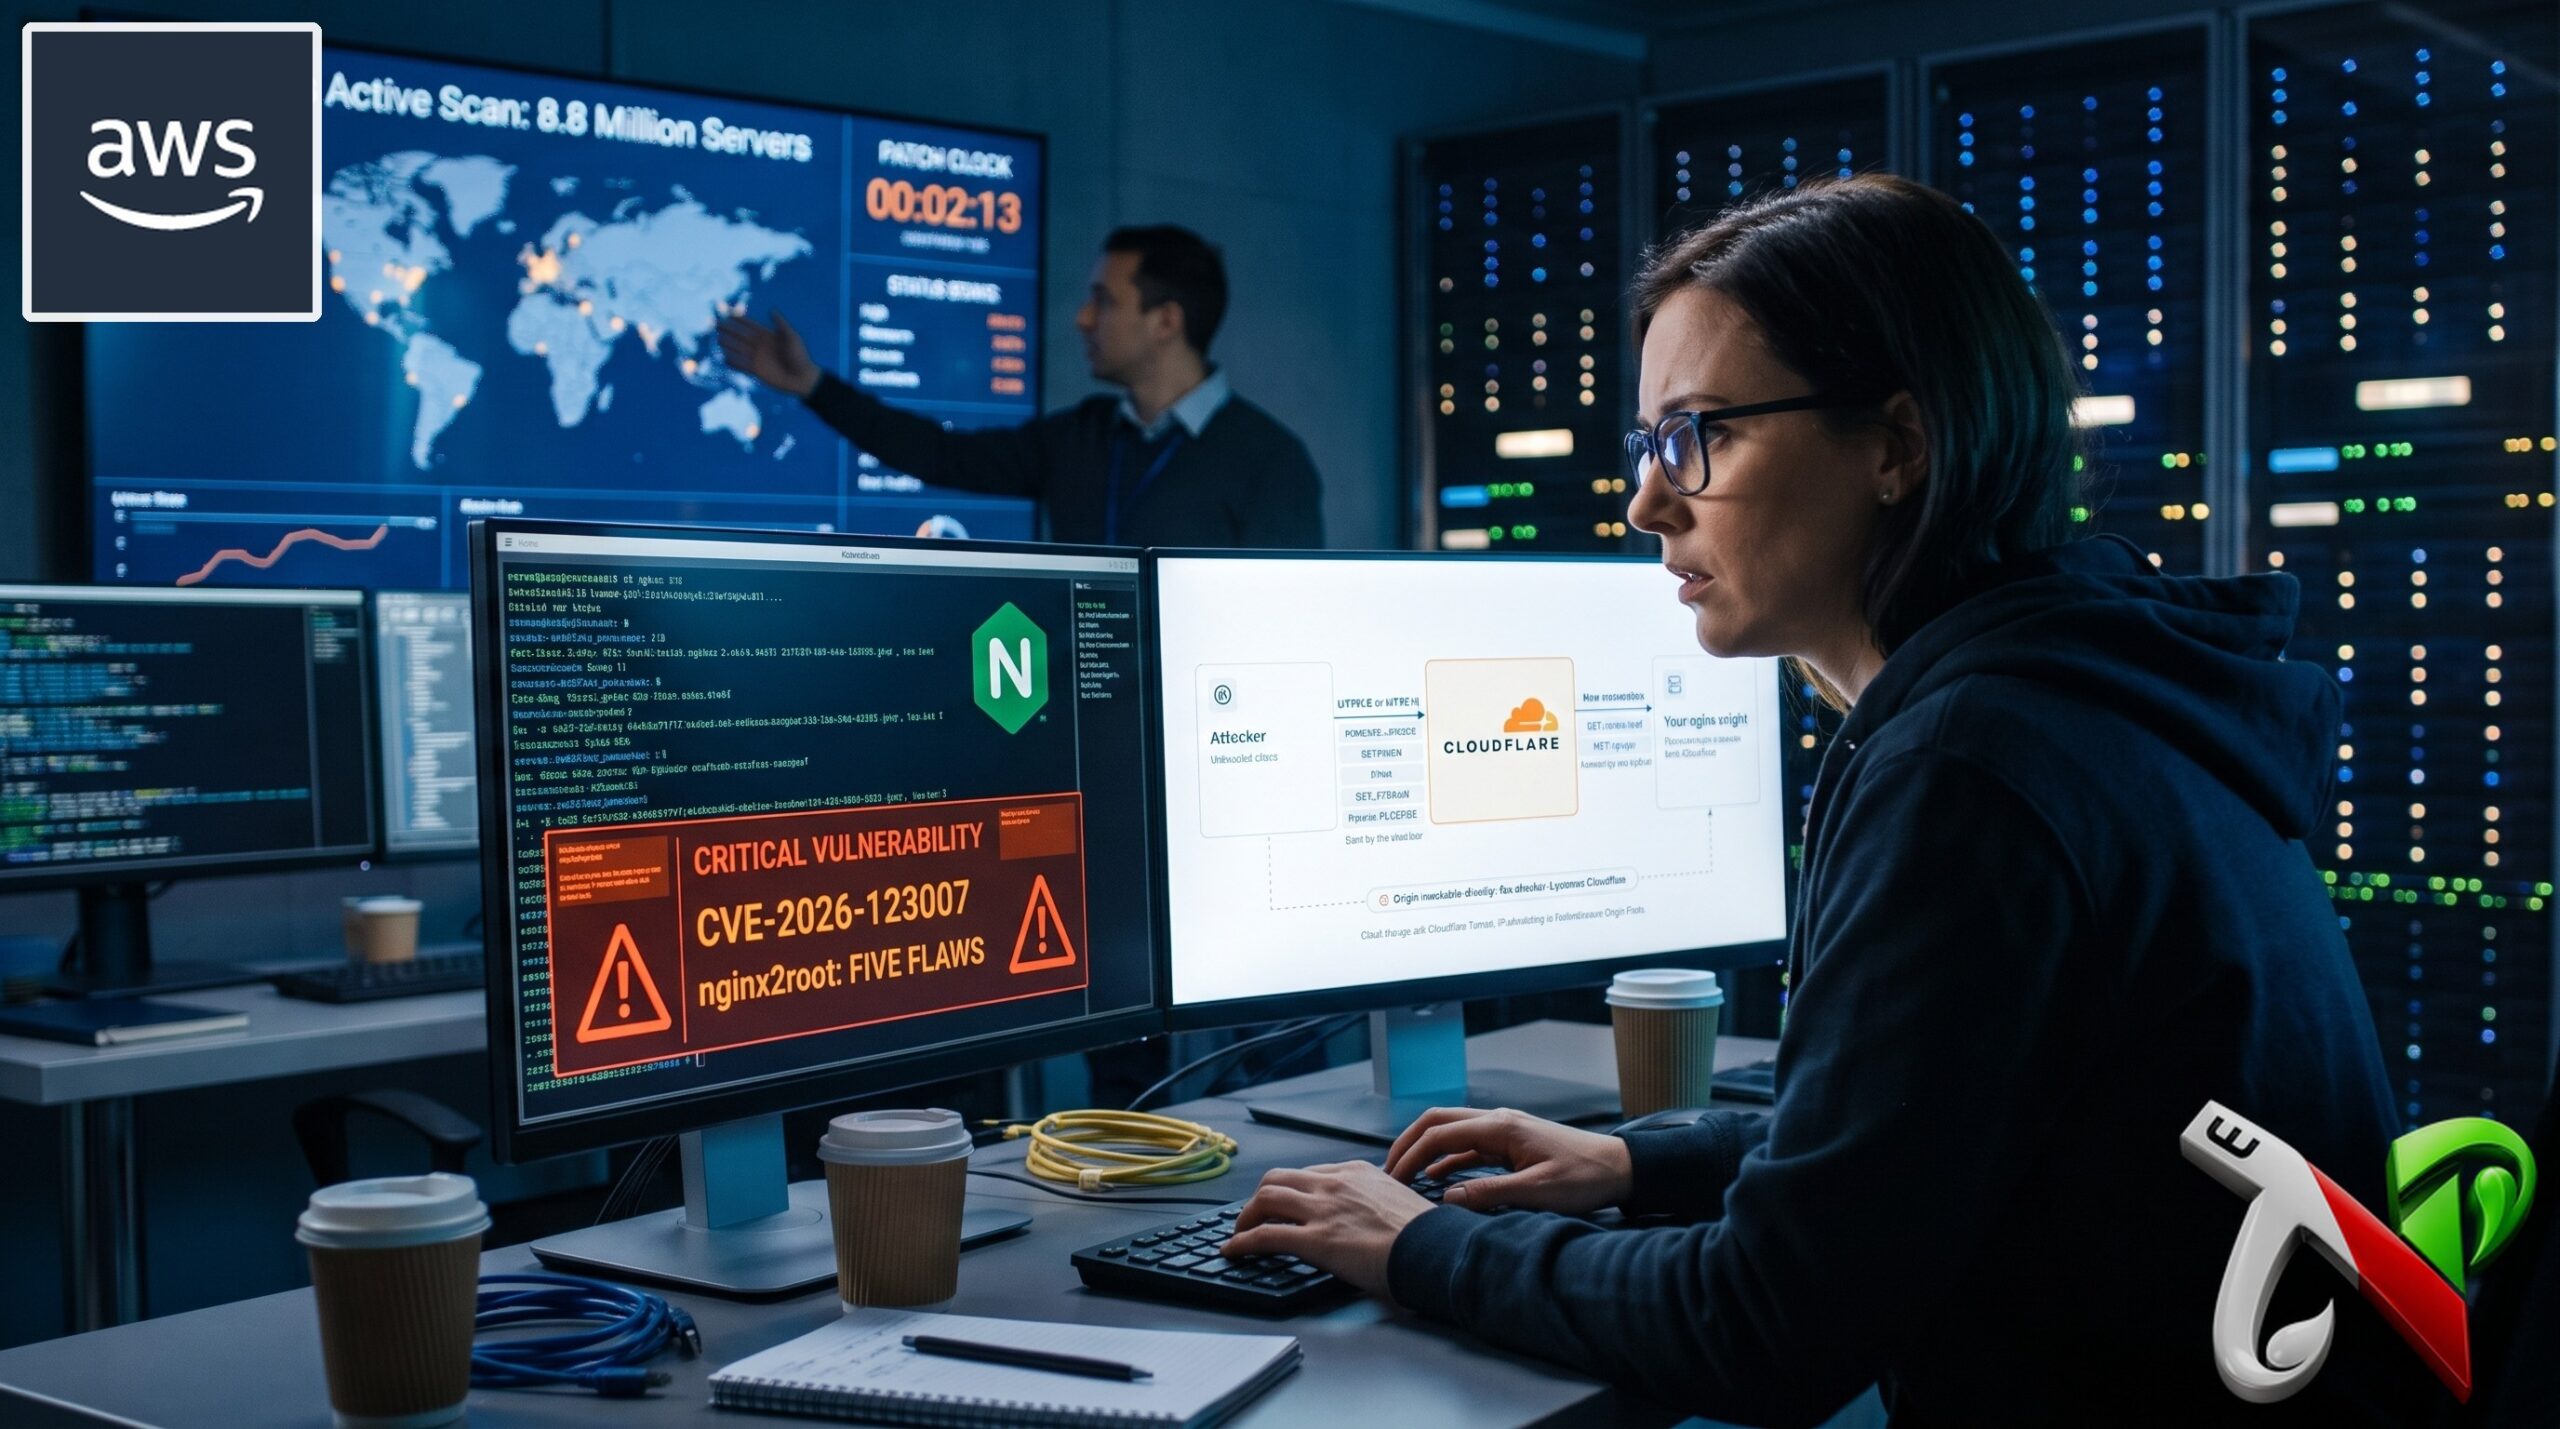
- The most serious, CVE-2026-123007, needs only HTTP/2 enabled and has existed since nginx 1.9.5. About 8.8 million services with a potentially affected version and HTTP/2 were counted by Censys as of November 19.
- Cloudflare says its own edge is not affected, and origins reachable only through its HTTP proxy are protected from the HTTP/2 and HTTP/3 attacks because the attacker's frames end at the edge.
- Admins should update to nginx 1.30.7 or 1.31.9 and restart, lock origins to Cloudflare via Tunnel, IP firewall rules or mTLS, and patch Spectrum and mail proxy setups directly, since the proxy does not cover them.
What Was Disclosed
The nginx2root name covers five independent memory corruption bugs, each of which works alone and depends on a different configuration. F5 grades them High under CVSS 3.1 and Critical under CVSS 4.0, and notes that code execution requires disabling or bypassing ASLR. In the case of CVE-2026-123007, Xint showed how leaked memory addresses can defeat that barrier. Other teams, including Rapid7 and Wiz Research, found the two HTTP/2 bugs independently.
The same nginx releases also fix five other flaws. The most notable, CVE-2026-118899, is an infinite loop when reading a request body over TLS 1.3 that lets an unauthenticated attacker stall a worker.
A Huge Exposed Footprint
CVE-2026-123007 is the one to worry about most. It requires only HTTP/2, which is common on TLS deployments, and it has been present in every release since HTTP/2 support arrived in 1.9.5. Xint ran its exploit across the public Internet against servers on AWS, GCP and Azure. A Shodan search on November 10 found 56.7 million hosts matching nginx, and of the 11.94 million reporting a version, 98.9% fell in the affected range. Version strings overstate risk because distributions backport fixes, but the exposure is still large.
There is also a kernel angle. Xint found a use-after-free in Linux’s SCTP send path, present since Linux 4.15 in 2018, that lets an attacker already running as the nginx worker gain root, even from inside a Docker container. Many distributions load the SCTP module automatically, so hosts that never use SCTP can still be exposed. As of November 18 no kernel fix existed, and Xint was withholding details.
None of the five CVEs was in CISA’s Known Exploited Vulnerabilities catalog as of November 19, and no exploitation in the wild had been reported. Rapid7 published a limited proof of concept, and fake exploits are circulating on GitHub.
Why the Proxy Helps
The dangerous bugs live in how nginx parses and manages HTTP/2 and HTTP/3 connections. Triggering them takes a carefully ordered stream of protocol frames sent directly to the nginx process, such as huge volumes of WINDOW_UPDATE frames, stalling SETTINGS frames, and well-timed stream resets. When a hostname is proxied through Cloudflare, that connection terminates at its edge. Cloudflare opens a separate connection to the origin and runs its own flow control, so a client cannot make it relay the attack traffic. Rapid7 reached the same conclusion about proxied connections.
Cloudflare also says its own edge is unaffected. Much of its proxy now runs on FL2, written in Rust, and it reviewed the remaining parts built on its modified nginx fork before disclosure, finishing a global update before the news went public.
Limits and Next Steps
The protection holds only if the origin cannot be reached directly. If an attacker finds the origin IP, Cloudflare is out of the path. The recommended fixes are Cloudflare Tunnel, firewall rules limited to Cloudflare’s IP ranges (set at the firewall, not in nginx), or Authenticated Origin Pulls with mTLS.
Some setups get no cover at all. Spectrum TCP/UDP applications pass traffic unmodified to the origin, and the nginx mail proxy handles IMAP, POP3 and SMTP, which Cloudflare’s HTTP proxy does not carry. For those, patch or disable the affected features, and restrict mail listeners to trusted networks. For everyone else, the advice is simple: upgrade to nginx 1.30.7 or 1.31.9, or your vendor’s fixed build, and restart.
Companies mentioned: AWS
Primary sources
 nginx2root: Five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them (blog.cloudflare.com) – A Cloudflare blog post explaining the November 18, 2026 disclosure of ten nginx vulnerabilities by F5 and nginx.org, five of which make up the Xint team's nginx2root research. It describes the memory corruption bugs, their CVSS ratings, the ASLR caveat for code execution, and the especially serious HTTP/2 flaw CVE-2026-123007, citing Shodan and Censys exposure figures. It also covers the companion Linux kernel SCTP use-after-free that enables root, the lack of known exploitation as of November 19, and the circulating fake exploits. The core of the piece is Cloudflare's position: its edge is unaffected, and origins reachable only through its proxy are shielded from the HTTP/2 and HTTP/3 attacks because the frames terminate at the edge. It lists ways to lock down origins, notes where protection does not apply (Spectrum, mail proxy), and urges updating to nginx 1.30.7 or 1.31.9. Published on blog.cloudflare.com by Dan Jones, Richard Boulton and Daniele Molteni.
 Powered by News Ranker
